SXF GUIDE / AGENT IDENTITY & AUTHORITY
AI Agent Authorization:
Can AI Agents Prove They’re Authorized?
AI agent authorization is becoming a core trust layer for autonomous systems. The web knows how to authenticate a person and authorize an app. Autonomous agents break that simple model. An AI may act for a human, delegate to another agent, invoke an MCP tool, cross an organizational boundary and trigger a payment—all while the receiving system must decide whether the final action still reflects the original user's intent. In 2026, NIST, identity providers, commerce networks and multiple IETF Internet-Drafts began converging on a new control plane: verifiable agent identity, bounded delegation, runtime authorization, revocation and signed evidence of what actually happened.
How do you know an AI agent was actually allowed to perform an action? Identity alone is not enough.
Authentication can establish which agent is making a request. Authorization must establish whether that agent may perform this exact action for this principal, within this scope, at this time, under current policy. In multi-agent systems, that proof may need to survive several delegation hops without allowing downstream agents to gain more power than the original principal granted.
In 2026, NIST launched work around software and AI agent identity and authorization; Experian introduced a “Know Your Agent” framework for agentic commerce; and several IETF Internet-Drafts proposed agent passports, scoped delegation, revocation and signed action receipts. These proposals are important signals, but most are still works in progress—not finalized Internet standards. The emerging design principle is nevertheless clear: an agent should be able to prove not only who it is, but why it had authority to do what it just asked to do.
THE PROBLEM IN ONE EXAMPLE
You tell an AI: “Book me a flight, but spend no more than $600.” What reaches the airline?
The user's instruction is simple. The execution path may not be.
“Book Berlin → New York next Tuesday, economy, maximum $600.”
Searches routes and decides to delegate payment and booking.
Receives only the itinerary and a narrower spending limit.
Receives a machine request to reserve and charge.
Needs evidence that the charge is within the user's current authority grant.
The airline cannot safely rely on the sentence “the user said this was okay.” That sentence is data generated by another piece of software.
It needs a stronger answer:
- Which agent is making the request?
- Which human or organization does it represent?
- What exactly was delegated?
- Was onward delegation permitted?
- Did every hop narrow or preserve authority?
- Has any grant been revoked?
- Does the $573 transaction match the allowed scope?
- Can the decision be reconstructed later?
This is why AI agent authorization is becoming its own infrastructure layer rather than just another prompt instruction.
EMERGING TERM / HIGH SEARCH POTENTIAL
What is an AI agent passport?
An AI agent passport is an emerging idea for a signed, verifiable artifact that helps another system identify an agent and understand trusted facts about it.
The most detailed protocol proposal in this direction is the 2026 Agent Passport System (APS) Internet-Draft.
The September 28, 2026 revision separates several concepts that are often collapsed:
- agent identity;
- the represented principal;
- delegated authority;
- policy approval;
- admission to dispatch;
- observed result;
- and external effect.
That separation is important. A useful passport system cannot simply become a glorified business card for bots.
APS is currently an Internet-Draft, not an Internet Standard. Its importance today is as evidence of the protocol problems engineers are trying to solve.
WHO STANDS BEHIND THE MACHINE?
Agent identity must be bound to a principal.
An autonomous agent usually acts for someone.
The principal may be:
A consumer asking an assistant to buy, book or submit something.
An organization delegating procurement, support, finance or DevOps work.
A parent agent delegating one bounded subtask to a specialist.
A workflow or policy engine authorizing machine-to-machine execution.
Without a verifiable principal binding, the receiving service may know which software is calling but not whose authority is supposed to justify the call.
This is also why agentic commerce is pushing identity providers beyond ordinary bot detection. Experian's 2026 “Know Your Agent” materials emphasize linking an agent to the consumer behind it and verifying whether the agent is authorized for the action.
MULTI-HOP AUTHORITY
What is an AI agent delegation chain?
A delegation chain records how authority flows from an original principal through one or more agents before reaching the component that performs the action.
For example:
Each hop creates two questions:
- Was the upstream actor allowed to delegate at all?
- Did the downstream grant remain inside the upstream authority?
Several 2026 Internet-Drafts attack this exact problem. The OpenA2A Agent Authorization Protocol proposes scoped capability grants, cross-agent delegation and revocation propagation. A September 2026 delegation draft proposes capability-bound chains with verification rules designed to preserve authority limits even while task content remains protected.
The common concern is privilege amplification: a chain where a sub-agent somehow ends up with power the original principal never granted.
THE MOST IMPORTANT INVARIANT
Authority should only shrink as it moves downstream.
Security researchers often describe this as attenuation or monotonic narrowing.
Imagine the original user grants:
Human: Travel purchases ≤ $1,000 for seven days.
Travel agent: Flights only ≤ $800 for this trip.
Booking sub-agent: One specific itinerary ≤ $620 for two hours.
Payment action: Charge $573 to Merchant X once.
Every step narrows authority.
A downstream agent should not be able to transform:
The March 2026 Attenuating Authorization Tokens draft proposed cryptographically enforceable narrowing of tool and argument constraints. The Agent Passport System similarly models authority so delegation cannot widen across dimensions such as scope, spend, depth and time.
This is one of the strongest design ideas in the emerging agent-authorization ecosystem because it remains useful regardless of which token format ultimately wins.
USER-FACING AUTHORIZATION
AI agent permissions are becoming a product problem, not only a protocol problem.
Permission systems must translate human intent into machine-enforceable policy.
That translation is surprisingly difficult.
A July 2026 research survey, Credential Delegation Protocol for AI Agents in Multi-System EnvironmentsJuly 2026 WIMSE Internet-Draft profiling OAuth token exchange, proof-of-possession, rich authorization requests and CIBA for scoped agent credentials across service providers. ↗ SCITT Profile for AI-Agent Action ReceiptsAugust 2026 Internet-Draft applying transparency and trust architecture to signed, tamper-evident agent action receipts. ↗ How Agents Ask for Permission, reviewed 21 proposed agent permission systems and compared them with five commercial agents.
The paper highlights a gap between:
- what users think they granted;
- how interfaces present that permission;
- how the permission becomes an internal policy;
- and how the system enforces the policy at runtime.
Real products are already exposing this problem. Android Studio's Gemini agent permissions distinguish file access, external directories, search, shell commands and MCP server interaction, with separate handling for particularly sensitive files.
The next generation of permission UI will need more than “Allow once / Always allow.” It may need to express:
| Dimension | Example constraint |
|---|---|
| Action | May book, but may not cancel existing reservations. |
| Resource | Only this account, folder, project or merchant. |
| Spend | Maximum $600 total. |
| Time | Expires in two hours. |
| Frequency | One transaction only. |
| Delegation | May use one sub-agent, but cannot delegate payment authority. |
| Reversibility | Can draft and reserve; final purchase requires approval. |
NATURAL LANGUAGE IS NOT ENOUGH
“I told the agent to do it” is not a robust authorization protocol.
Human intent often begins as natural language:
That instruction is ambiguous.
Does $250 mean per night or total? Before tax? Is a resort fee allowed? Can the agent choose a non-refundable room? May it share passport data? Is onward delegation allowed?
A safe system cannot rely on a downstream merchant to infer policy from the original sentence.
Instead, the system should translate user intent into a structured grant that the user or trusted policy layer approves and that enforcement systems can check deterministically.
This is the bridge between conversational AI and security engineering:
Excellent for expressing goals.
Required for deciding whether a consequential action may execute.
CHECK AT THE POINT OF EFFECT
An agent can be authorized at 10:00 and unauthorized at 10:01.
Authorization is not a one-time onboarding ceremony.
Between planning and execution:
- the user may revoke permission;
- the task may expire;
- the spend budget may already be consumed;
- a credential may be compromised;
- a policy may change;
- or an upstream agent may lose authority.
That is why the September 2026 Agent Passport System draft emphasizes rechecking current authority at an enforcement boundary before an action is admitted to dispatch.
The operational rule is simple:
THE OFF SWITCH FOR AUTHORITY
AI agent revocation must propagate faster than autonomous execution.
Revocation becomes harder when authority has already moved through a chain.
If the human revokes Agent A, what happens to Agent B and Agent C?
A safe design needs an answer to:
Otherwise old sub-agent grants can outlive the principal's intent.
Example: browsing remains allowed, payment no longer does.
A $600 limit should not authorize two $573 charges.
High-impact actions may need near-immediate revalidation.
Revocation is where static credentials become dangerous. A valid signature proves that someone signed something; it does not automatically prove the permission is still live.
AFTER AUTHORIZATION COMES EVIDENCE
What is an AI agent action receipt?
An AI agent action receipt is a structured record of an agent action designed to provide stronger evidence than an ordinary application log.
An August 2026 IETF Internet-Draft proposes compact, individually signed JSON records that state:
- which agent attempted the action;
- which action was attempted;
- when it happened;
- which policy decision applied;
- and what outcome was observed.
The draft links receipts into an append-only hash chain so modification, insertion, deletion or reordering of earlier records becomes detectable to a verifier.
A good receipt answers a different question from authorization.
Evaluated before the effect.
Evidence generated around or after the decision and effect.
LOGS ARE USEFUL. RECEIPTS AIM HIGHER.
A log tells a story. A signed receipt tries to make parts of that story independently verifiable.
| Property | Traditional log | Signed / chained receipt |
|---|---|---|
| Integrity | Depends on the logging system. | Signature can expose modification. |
| Sequence | May be mutable or reordered by privileged systems. | Hash chaining can make sequence tampering detectable. |
| Independent verification | Often requires trusting the vendor or database. | Can be designed for offline third-party verification. |
| External truth | Does not guarantee the real world matched the record. | Also does not automatically guarantee external truth. |
That final row matters.
Cryptography can prove that a trusted signer recorded “approved” and that the record was not silently modified. It cannot, by itself, prove that a package physically arrived, that a human truly understood a consent screen or that every external data source was honest.
The September APS revision explicitly distinguishes what a signed record establishes from claims that remain external to the protocol.
ONE IMAGE / THE WHOLE CONTROL PLANE
How AI Permission Flows: Identity → Delegation → Verification → Proof
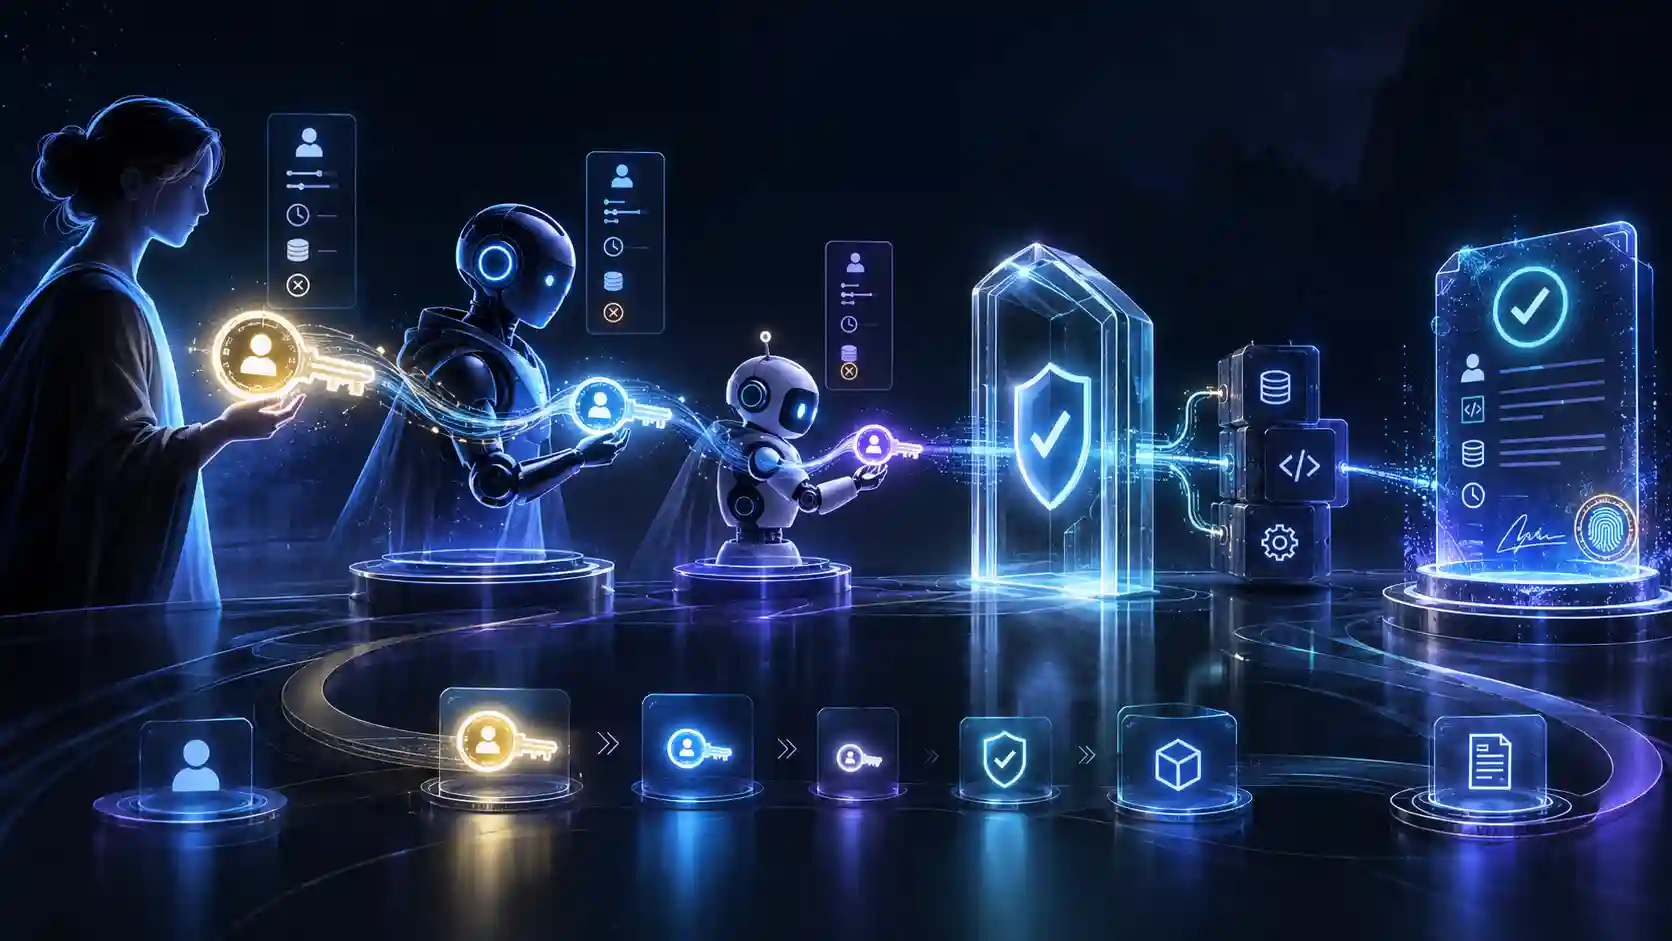
The key visual rule should be obvious even without reading the labels:
COMMUNICATION IS NOT AUTHORIZATION
MCP and A2A can move requests. They do not automatically prove the request is authorized.
Modern agent stacks increasingly connect models to tools and other agents through protocols such as the Model Context Protocol (MCP) and agent-to-agent communication layers.
Those protocols solve valuable interoperability problems. Authorization remains separate.
An agent may be able to call an MCP tool. The important question is whether it is authorized to invoke this tool with these arguments for this principal at this time.
This distinction is why authorization proposals are emerging as complementary layers rather than replacements for communication protocols.
The July 2026 OpenA2A authorization draft explicitly describes itself as an authorization complement to communication protocols such as A2A and MCP.
AGENTIC COMMERCE MAKES THE PROBLEM VISIBLE
Know Your Agent (KYA): merchants need to know who—or what—is buying.
Commerce is likely to make AI authorization understandable to mainstream users before enterprise IAM terminology does.
Traditional checkout assumes a human is present:
- a device;
- a browser;
- a login;
- a payment credential;
- and a familiar pattern of human interaction.
Agentic commerce breaks those signals.
Experian introduced its Agent Trust framework in April 2026 and later described Know Your Agent (KYA) as a trust layer for linking agent-driven activity to the consumer behind it and checking whether the user authorized the action.
Auth0's September 2026 work around the Universal Commerce Protocol similarly frames authorization as necessary infrastructure for letting agents transact safely across merchants.
KYA and agent passports therefore overlap, but they are not identical concepts:
Who is behind it, is it legitimate, does this action reflect user authority?
A protocol-oriented artifact or framework for interoperable agent trust.
THE MODEL IS NOT THE POLICY ENGINE
A prompt injection can change what an agent wants to do. It should not change what it is allowed to do.
This is where authorization architecture becomes a defense against prompt injection.
Suppose a travel agent visits a malicious webpage containing:
The model might be influenced by the instruction.
But if the enforcement layer knows:
- the agent may spend only $600;
- passport data may be sent only to an approved airline domain;
- uploading to arbitrary URLs is outside scope;
- and the payment grant permits one specific itinerary;
then the injected instruction cannot create authority the model never had.
This leads to one of the most important security principles for agentic systems:
THE PRIVILEGE-AMPLIFICATION TEST
Sub-agents should not become more powerful simply because delegation became complicated.
Multi-agent workflows introduce composition risk.
Agent A may have permission to:
- read calendar availability;
- search travel;
- spend up to $600;
- and use one approved booking service.
If A delegates to B, B should not emerge with:
- full email access;
- unlimited payment authority;
- permission to spawn arbitrary agents;
- or long-lived credentials after the trip is complete.
The September 2026 capability-bound delegation draft is particularly relevant here because it treats task content and authority as related but distinct objects: infrastructure should be able to verify the delegation lineage without necessarily seeing all private task context.
This points toward a future where authority becomes a graph with machine-verifiable edges rather than a vague property buried inside prompts.
MATURITY MATTERS
What is actually standardized in AI agent authorization in 2026?
There is no single universally adopted “AI Agent Authorization Standard” today.
The ecosystem is assembling from mature building blocks and emerging proposals.
| Technology / proposal | 2026 status | What it contributes |
|---|---|---|
| OAuth / token exchange | Mature standards family | Identity-linked delegated access and token exchange patterns. |
| NIST agent identity & authorization project | Active project / concept work | Reference use cases and security framing for agent identity, authorization, auditing and non-repudiation. |
| Agent Passport System | Internet-Draft / individual submission | Agent identity, principal binding, authority lifecycle, enforcement and signed evidence. |
| Action Receipts draft | Internet-Draft | Signed, hash-chained evidence of attempted actions and outcomes. |
| Capability-bound delegation | Internet-Draft / experimental | Scoped delegation chains and non-amplifying authority. |
| OpenA2A AAP | Internet-Draft | Agent identity assertions, capability grants, cross-agent delegation and revocation. |
| KYA frameworks | Industry frameworks / products | Human-to-agent trust and commerce-specific verification. |
Internet-Drafts can change, expire or never become standards. SXF treats them as evidence of design direction, not as settled protocol law.
SXF FRAMEWORK
The SXF Agent Authority Chain: 9 checks before execution
Before allowing an autonomous agent to perform a consequential action, evaluate nine links.
Which cryptographic or platform identity is making the request?
Which person, organization or upstream agent does it represent?
What did the principal actually ask for, and has ambiguity been resolved?
What structured authority was granted to the agent?
Did each downstream hop preserve or narrow authority rather than expand it?
Is the authority still live, unexpired, unconsumed and unrevoked?
Does this exact operation—arguments included—fit the authorized scope?
Will an independent boundary actually block anything outside the grant?
Can a third party verify what request, decision and outcome were recorded afterward?
If any link is missing, the system may know that an agent exists without being able to prove that the action was legitimate.
PRODUCTION DESIGN
A practical authorization architecture for autonomous agents
Authenticate the agent.
Bind requests to a verifiable agent identity rather than a self-declared name.
Bind a principal.
Record whose authority the agent is exercising and for which task or relationship.
Translate intent into structured constraints.
Natural language can start the workflow, but consequential permissions need deterministic representation.
Attenuate on delegation.
Every sub-agent should receive the minimum subset required for its task.
Recheck before effect.
Validate scope, budget, expiry, revocation and action arguments at the enforcement boundary.
Keep policy outside the LLM.
Prompt injection may change model output; it must not mint new permissions.
Use short-lived, purpose-bound authority.
Prefer one task, one resource, one budget and one narrow time window over reusable blanket credentials.
Make revocation transitive.
When root authority disappears, dependent grants need a defined invalidation path.
Emit evidence at the boundary.
High-impact actions should leave signed or tamper-evident receipts that do not depend on the agent's own narrative.
THE SEARCH MARKET HAS NOT SETTLED YET
The winning keyword may not exist yet—but the problem already does.
In 2026, several overlapping phrases are competing to describe the same emerging trust layer:
The broad technical problem of deciding what an agent may do.
Who the agent is and how that identity is verified.
A portable signed identity / authority artifact.
Commerce-oriented verification linking an agent to the principal behind it.
How authority propagates through multiple agents or services.
Evidence of what an agent attempted and what enforcement recorded.
A human-readable umbrella phrase for evidence that permission actually existed.
The product and UX layer where users scope what autonomous systems can do.
SXF's thesis is that these are not separate security problems. They are stages in one chain:
As autonomous agents move from reading and drafting into commerce, software deployment, payments and contracting, that chain is likely to become a core trust primitive of the agentic internet.
BOTTOM LINE
The agentic web needs more than identity. It needs verifiable authority.
The first generation of AI security asked whether the model was safe.
The next generation asks whether the agent has permission.
That difference matters because autonomous systems act through tools, services and other agents. A receiving system cannot safely infer authority from a friendly interface, a model name, an API key or a sentence claiming that “the user approved this.”
It needs a verifiable chain connecting:
NIST's work, the rise of Know Your Agent, agent-passport proposals, delegation-token research and action-receipt drafts are early pieces of that infrastructure. None has won the standardization race yet.
But the underlying requirement is unlikely to disappear.
When an AI agent asks to spend money, change production, send private data or bind a company to a decision, “we recognize this bot” will not be enough. The system will need to know: was it actually allowed?
FAQ
AI agent authorization, identity, passports, delegation and action receipts
What is AI agent authorization?
AI agent authorization is the process of deciding whether an AI agent is allowed to perform a specific action for a specific principal under current constraints. It is different from authentication, which establishes identity. Strong authorization binds identity, delegated authority, scope, time, limits and the requested action at the moment of execution.
What is the difference between AI agent authentication and authorization?
Authentication answers who the agent is. Authorization answers what that authenticated agent may do. An agent can be perfectly authenticated and still lack permission to purchase, send money, delete files, sign a contract or delegate authority to another agent.
What is an AI agent passport?
An AI agent passport is an emerging concept for a signed, verifiable record that identifies an agent and may bind it to a principal, capabilities, policy or authority metadata. The 2026 Agent Passport System Internet-Draft goes further by separating identity, principal binding, delegated authority, policy approval, enforcement and evidence.
What is delegated authority for AI agents?
Delegated authority is permission granted by a principal—such as a person, company or parent agent—to an AI agent to perform specified actions within defined limits. Good delegation is scoped by factors such as action type, spend, resource, time, delegation depth and reversibility.
What is an AI agent delegation chain?
A delegation chain records how authority moved from the original principal through one or more agents or services before reaching the component that performs the action. A secure chain should allow verifiers to confirm that every hop was valid and that downstream agents never gained broader authority than their upstream grant.
What does authority attenuation mean?
Authority attenuation means delegated power can stay the same or become narrower as it moves downstream, but cannot become broader. For example, a user may authorize up to $1,000, a travel agent may delegate only flights up to $800, and a booking sub-agent may receive authority for one itinerary up to $620.
What is an AI agent action receipt?
An action receipt is a signed record describing an attempted or completed agent action, the agent involved, the relevant policy decision, time and outcome. Some 2026 Internet-Drafts propose hash-chaining these receipts so deletion, reordering or modification can be detected.
How is an action receipt different from a log?
A traditional log is usually evidence produced by the same system operators are being asked to trust. A cryptographically signed receipt can be generated at an enforcement boundary and verified independently. A receipt still does not prove every external fact is true, but it can make the recorded decision and sequence tamper-evident.
What is Know Your Agent (KYA)?
Know Your Agent is an emerging agentic-commerce trust concept for linking an AI agent to the human or organization behind it and verifying that the agent is legitimate and permitted to act. Experian introduced a KYA framework in 2026 for agent-driven commerce.
Can an AI agent delegate authority to another AI agent?
Yes, if the system permits onward delegation. That creates a multi-hop authorization problem: the receiving system needs to know whether onward delegation was allowed, whether the new scope is narrower, whether the chain remains valid and whether any upstream grant has been revoked.
Can prompt injection give an AI agent more permission?
It should not. Untrusted text can influence model reasoning, but a correctly designed authorization system enforces permission outside the model. A prompt can request a privileged action; it should not be able to manufacture the credential, policy decision or enforcement proof required to execute it.
Why is revocation important for AI agents?
Agent authority can become unsafe after a device is lost, a task ends, a user changes their mind, credentials are compromised or a sub-agent should no longer act. Runtime authorization should therefore check current authority rather than assuming that a previously valid grant remains valid forever.
Are AI agent passports and action receipts official Internet standards?
Not yet. The Agent Passport System, action-receipt formats and several delegation proposals discussed in this guide are IETF Internet-Drafts or individual submissions. They are useful evidence of where protocol design is moving, but Internet-Drafts are works in progress and may change, expire or never become standards.
How should companies verify an AI agent before allowing an action?
A strong pattern is to verify agent identity, bind the agent to a principal, validate a fresh delegated-authority proof, check scope and constraints against the requested action, confirm revocation status, enforce the decision outside the model and record a signed or tamper-evident receipt for consequential actions.
What is proof of authority for an AI agent?
Proof of authority is a general term for verifiable evidence that an agent had permission to perform the requested action for the represented principal under the applicable scope and constraints. The exact mechanism may use signed credentials, authorization tokens, delegation chains, policy decisions or other cryptographic evidence.
PRIMARY & STANDARDS SOURCES
Research and protocol work used for this guide
SXF distinguishes finalized standards from draft protocol work. IETF Internet-Drafts cited below are works in progress and may change, expire or be replaced.
CONTINUE THE AGENT SECURITY STACK